A defined framework for converting verified breaches into controlled operational responses
Breach Activation Response—BAR—is Guardian Edge Technologies’ defined process for moving from a verified security event to accountable action. It establishes triggers, roles, escalation paths, dispatch procedures, evidence handling and reporting so that an alert does not stop at acknowledgement.
Organisations that require a documented, auditable process connecting monitoring, response personnel, site contacts, management and authorities.
We begin with a site and risk assessment, confirm operational priorities and design a proportionate solution. The proposal defines the equipment or personnel required, implementation scope, responsibilities, commissioning requirements and ongoing support options.
Breach Activation Response can operate independently or connect with Guardian Edge monitoring, analytics, response, connectivity and managed IT. Integration is based on the client’s risk profile and agreed procedures—not added simply for complexity.
Each stage creates a defined action and an operational output.
| Stage | Action | Output |
|---|---|---|
| 1. Detect | Camera, alarm, sensor, person or client reports an event. | Security event created. |
| 2. Verify | Controller confirms or reasonably assesses whether the event is genuine. | Verified, unverified or false-alarm classification. |
| 3. Activate | The appropriate response protocol is initiated. | Response activation record. |
| 4. Dispatch | Response personnel or partner receive the location and incident information. | Dispatch timestamp and acknowledgement. |
| 5. Coordinate | Control room maintains communications and monitors available systems. | Live incident log. |
| 6. Stabilise | Response confirms the site condition and immediate risk status. | Confirmed site status. |
| 7. Escalate | Police, client, management or other parties are contacted where the contract or procedure requires. | Escalation record. |
| 8. Close | The incident is closed only after required checks and records are complete. | Closed incident record. |
| 9. Report | The client receives the agreed report and evidence package. | Incident or management report. |
| Priority | Example | Response treatment |
|---|---|---|
| P1 Critical | Confirmed intrusion with an active threat, violence, fire, life-safety risk or major infrastructure compromise. | Immediate escalation and dispatch under the contracted procedure, with management notification. |
| P2 High | Confirmed intrusion, theft in progress or significant security breach without an immediate threat to life. | Immediate activation and response. |
| P3 Medium | Suspicious activity, repeated alarm or unconfirmed breach requiring physical verification. | Verification and controlled response. |
| P4 Low | Technical alarm, maintenance issue or non-security alert. | Technical or administrative handling; no emergency response unless conditions change. |
Activation authority is documented in each client’s site response matrix. Depending on the contract design, a verified event may allow the controller to activate response directly, while ambiguous or high-risk events may require escalation to a supervisor.
The objective is to avoid unnecessary delay while maintaining accountability. The response matrix defines who may activate, who must be notified, which resources may be dispatched, when external authorities should be contacted and what evidence must be retained.
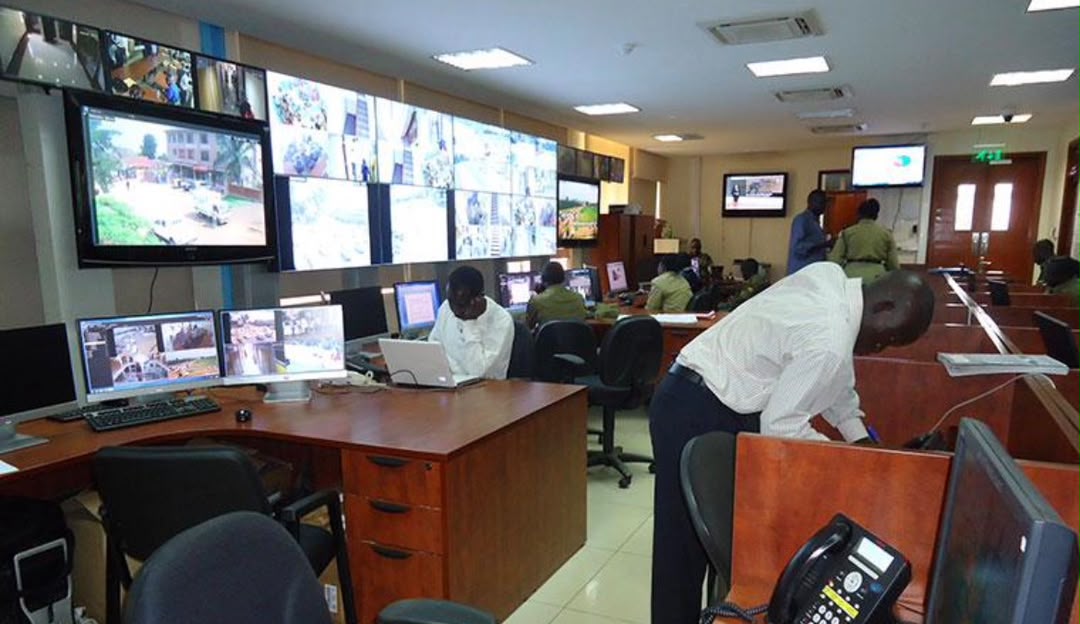
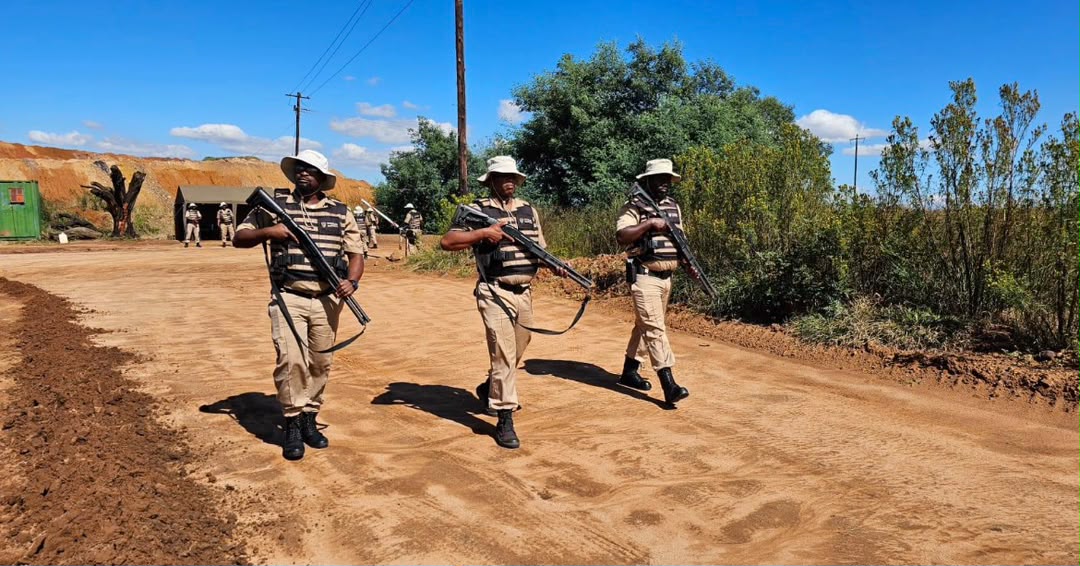
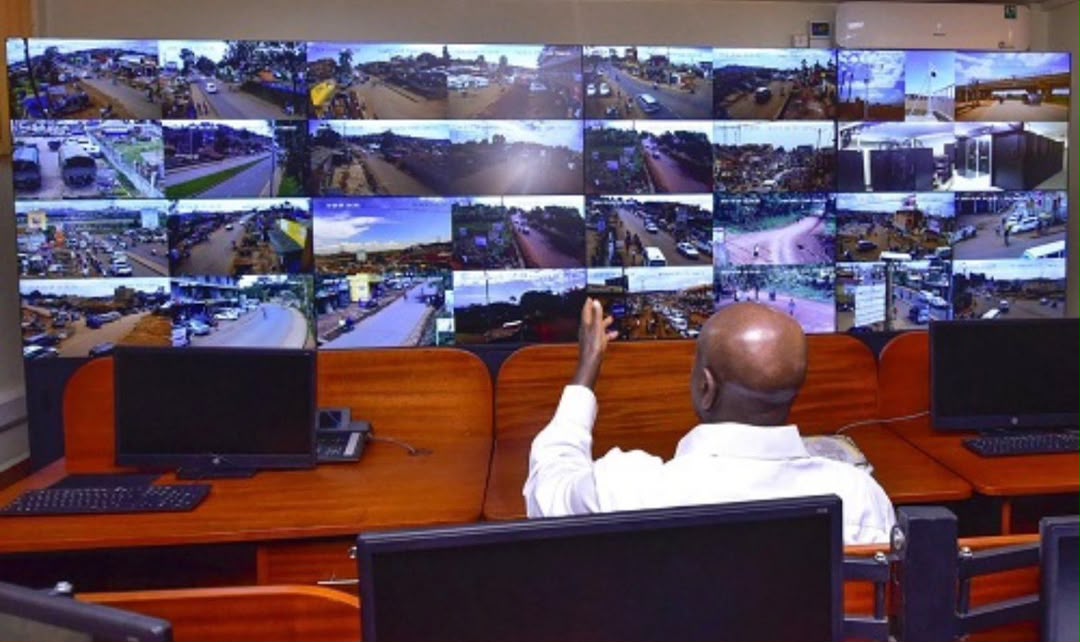
Photography is placed with the service it represents, showing the operational environments and capabilities supported by Guardian Edge.